thesabear
fb85d9c8f5
Access model now covers the narrowly-scoped read-only utility policies
(ansible sync roles, metrics-reader, pki-reader) alongside the
host-scoped svc-* pattern - the fuller picture confirmed live against
Vault's actual ACL policy list, not just the original narrower claim.

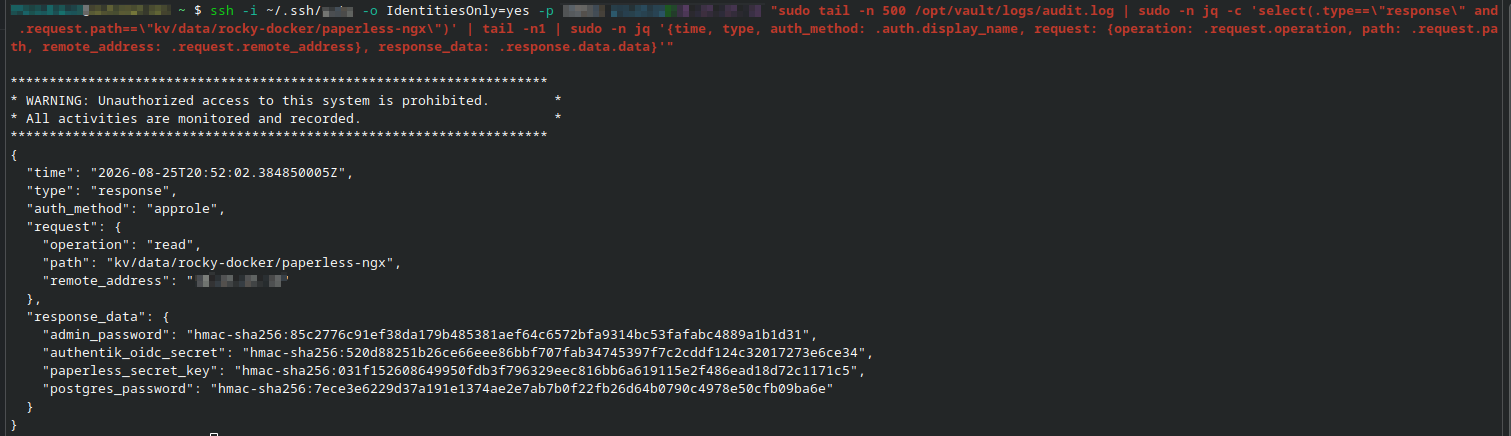
Added two real screenshots: the live policy list, and an actual audit
log entry showing a KV read with every secret value as hmac-sha256:...
instead of plaintext - proof for the audit-trail claim instead of just
an assertion of it.
72 KiB
1511x436px
72 KiB
1511x436px