thesabear
3e91e426d1
Source Trilium notes (Authentik/SSO Integration, Gitea Access Model)
live-verified and stamped this session - authentik_api_token confirmed
in vault.yml, automation-bot confirmed as a real non-admin Gitea account
via the API.

Cut the redundant Mermaid diagram (prose right below it said the same
thing). Restored the LDAP/superuser-outpost exception from the source
note as a compact callout rather than a full section, proportionate to
its actual weight. Added the real reasoning for centralizing auth and
the proxy-layer defense-in-depth argument, a table of the ~9 apps
running real native OIDC/SAML on top of the universal Proxy Provider
baseline (corrected after initially misstating it as either/or), the
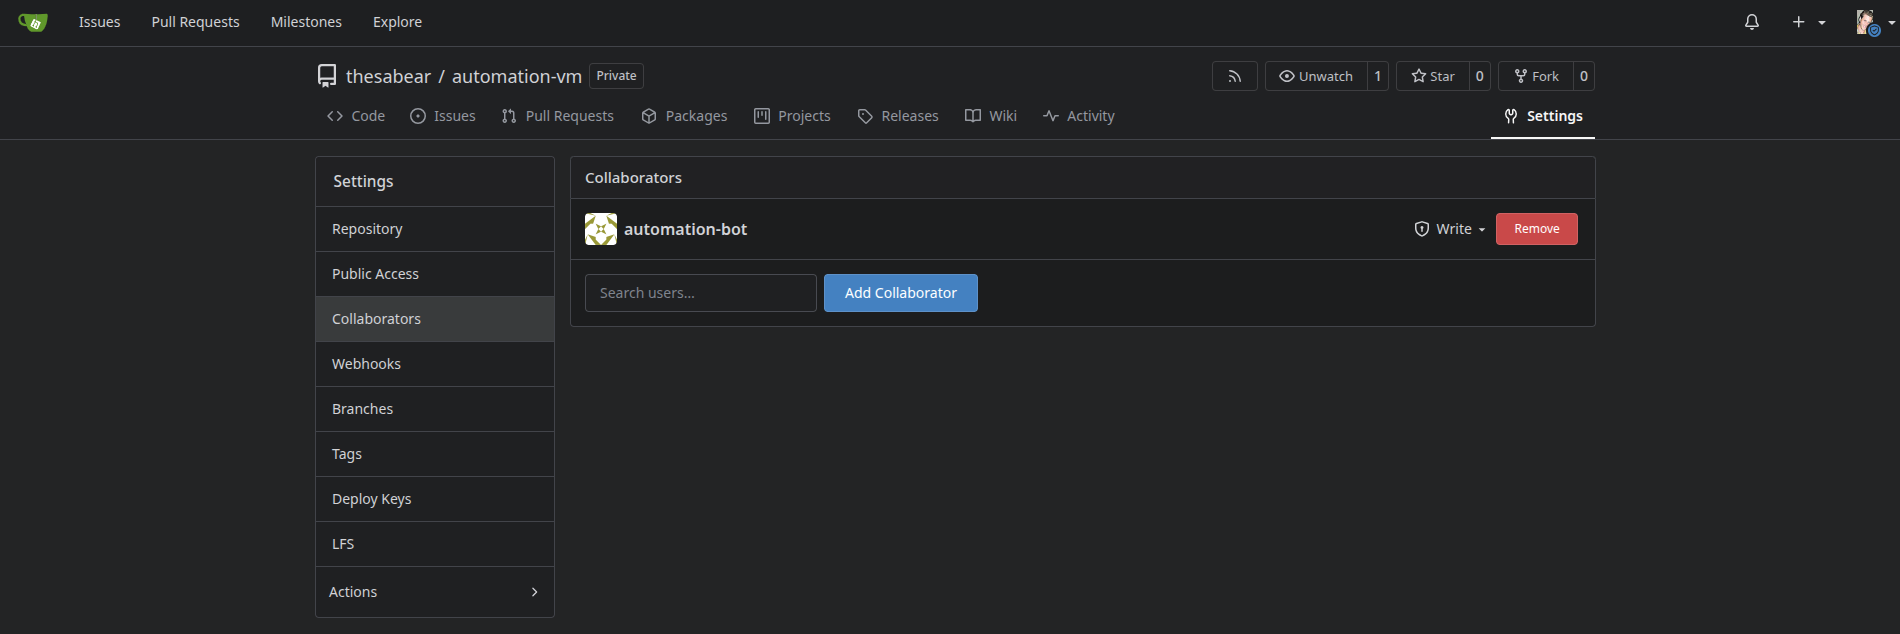
provider-removal discipline, and two screenshots proving the Write/
Read-only access split instead of just asserting it.
66 KiB
1900x634px
66 KiB
1900x634px